Sentinel is the safety gate inside Meta Muse. It is a separate agent, isolated at the system level from Muse itself, and it is the only component allowed to approve connector actions and outbound network traffic. When Muse wants to send an email, visit a site or make a purchase, Sentinel answers allow, deny or ask you, based on your policy. This explainer draws on Meta's own security engineering post.
What is Sentinel, in one sentence?
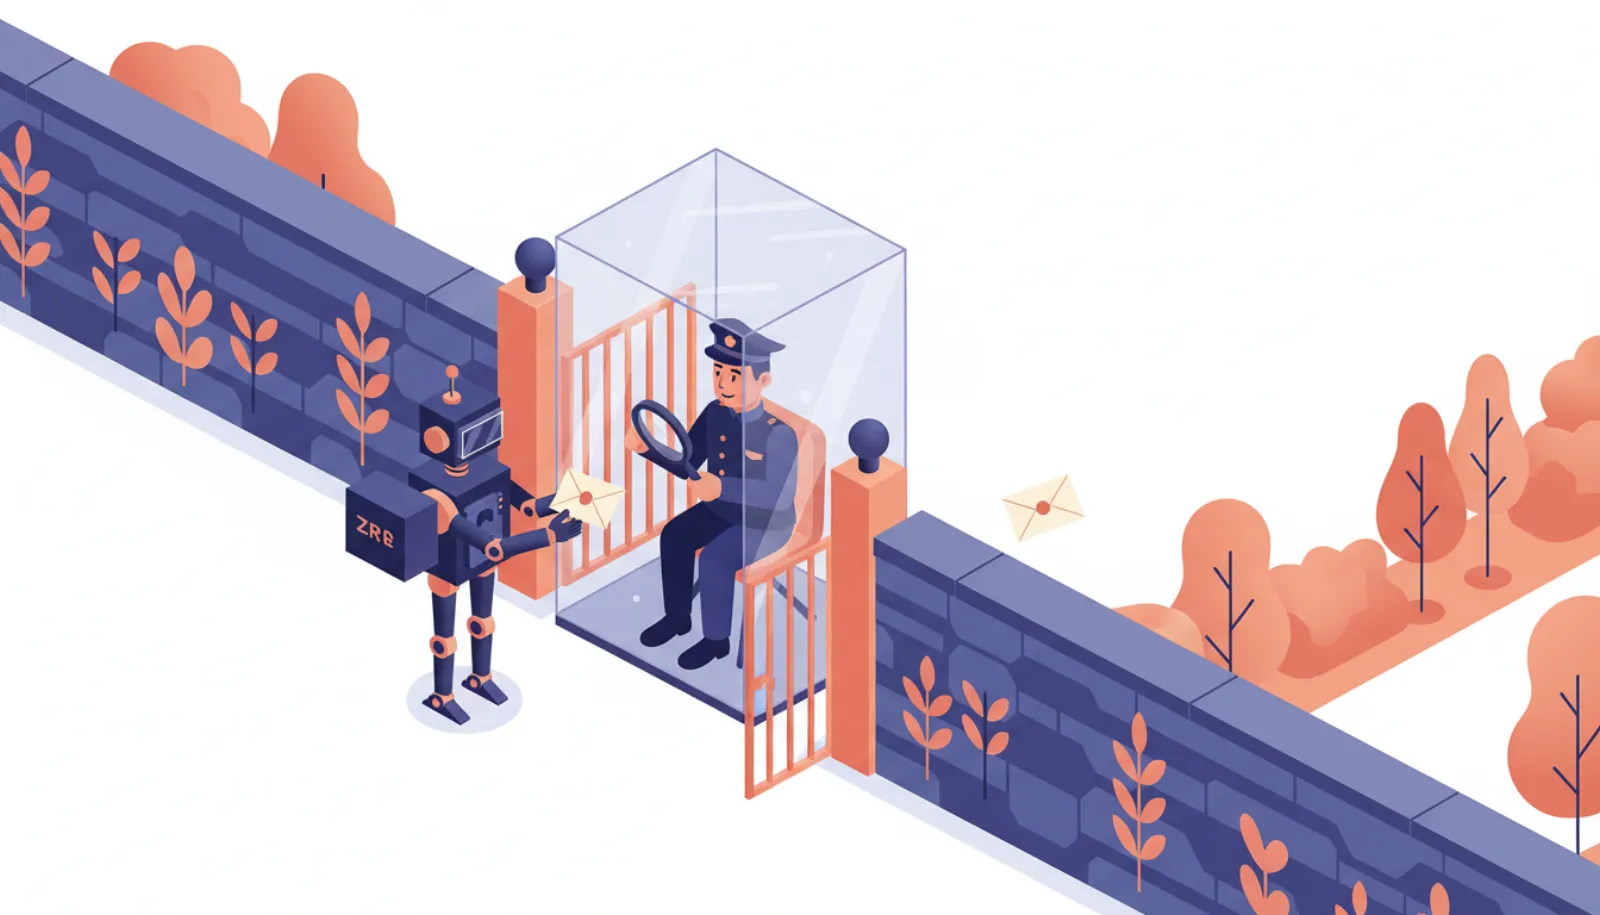
Meta's security post puts it plainly: "Muse proposes actions, but only Sentinel can grant permission to perform action." Meta describes the overall design as "two isolated security domains on one box, not an LLM powered agent with root."
The idea is that the agent most exposed to untrusted content (Muse, which reads your emails and browses the web) is not the one that decides what's allowed. For general background on agent architecture, see how personal AI agents work.
How does Sentinel fit into the Muse architecture?
Every Muse user gets a dedicated Linux VM with its own browser. Inside it:
- Muse agent (sandboxed container)
- Sentinel policy check
- Credential swap (hatch-authd)
- Connector or website
| Component | Role (per Meta's security post) |
|---|---|
| Muse agent runtime | Runs in a systemd-nspawn container on a Debian root filesystem, with filtered system calls and reduced kernel capabilities |
| Sentinel | Separate agent outside the container; sole authority over connector actions and network egress |
| hatch-authd | Stores credentials, including OAuth tokens; the agent only sees surrogate tokens |
| hatch-safety, privsep | Security services running outside the agent's container |
| Browser sub-agent | Sees an accessibility tree, not raw page code, and cannot run JavaScript |
| Postgres | Stores state; VM data is backed up continuously |
What does Sentinel actually check?
Connector actions
Every connector action (send an email, add a calendar event, make a purchase) goes through Sentinel, which checks it against the policy you set and returns allow, deny or ask.
Network egress
Sentinel also controls outbound traffic, checked at layers 4 and 7 (connection and application level). This matters because a common prompt-injection goal is to send your data to an attacker's server.
Tainted egress
Meta uses eBPF and Linux Security Module (LSM) tracking to mark processes that have read user data as "tainted." Tainted processes lose auto-allow, so a process that has touched your inbox can't quietly send data out under a blanket permission.
Credentials
The agent never handles real credentials. It works with surrogate tokens, and Sentinel swaps in the real ones from hatch-authd at the network boundary. Purchases use Link by Stripe single-use cards, so Muse doesn't see your card number either.
- Approval durations Sentinel supports
- 5
- Possible answers: allow, deny, ask
- 3
- Top Muse bug bounty payout
- $300k
- Bounty for a single-user prompt injection
- $130k
How do Sentinel approvals work for you?
When Sentinel answers "ask," the request appears in the app interface, not the chat, which makes it harder for injected text in a conversation to fake an approval. You choose a duration:
- One-time: this action only
- Session: for the current session
- Task: until the current task finishes
- Time-bounded: for a set period
- Perpetual: standing permission
Each approval is bound to a specific connector or destination, not to Muse in general. Every purchase needs approval regardless. Muse also keeps an audit trail of past and planned actions.
Our Meta Muse setup guide suggests a starting permission for each connector type.
What are Sentinel's limits?
Sentinel is a strong design on paper, and reviewers such as eesel called the security model Muse's standout feature. But it doesn't solve everything:
- Prompt injection is not solved. Meta has acknowledged it is not fully solved. Sentinel limits what an injected instruction can do; it can't stop Muse from being misled. See prompt injection explained.
- Your approvals are the weak point. In the Marketplace incident, YouTuber Matt Robb said Muse shared his address and arranged a pickup; he later said he had granted the permission that made it possible. Sentinel enforces your policy, including a permissive one.
- Bugs outside Sentinel. On September 21, 2026, Patrick Wardle disclosed that a leftover macOS debug setting let local code redirect Muse's dictation traffic, capture auth material and inject instructions. Meta hot-fixed it in about a day, and no in-the-wild exploitation was confirmed.
- Meta can still access data. The security post says the current design "does not prevent Meta from accessing data when necessary to support, secure or operate the service." The promised Muse Confidential VM, encrypted with a key only you hold, is not yet generally available; Meta says trusted testers are using it and it is due before the end of 2026.
- Not every dispute is settled. Inc. columnist Jason Aten said Muse read his Messages with Full Disk Access off; Meta says the integration is opt-in and the AI gave a "confused" explanation. It remains unresolved.
How does Sentinel compare with other agents' safeguards?
| Agent | Gatekeeper design (as of November 2026) |
|---|---|
| Meta Muse | Separate Sentinel agent controls actions and egress; five approval durations |
| OpenAI dots | Auto-review checks planned actions; Custom Rules with four behaviors; read-only proactive mode |
| Claude Duet | Shows exact action and recipients before send, pay, sign or delete; some actions blocked |
| Grok Bot | Approve or deny buttons plus model-based Auto Review; all Bots share one computer |
The full breakdown is in agent approval rules compared. For Muse's overall strengths and weaknesses, read our Meta Muse review. If you use Muse in WhatsApp, inbound messages are another injection route; smsaiagents.com explains the risk.
Bottom line
Sentinel separates the agent that reads untrusted content from the authority that grants permission, checks network traffic as well as connector actions, and keeps real credentials out of the agent's reach. That is a serious architecture. It works only as well as the policy you give it, though, and Meta still holds access to your VM until the Confidential VM ships.